For cybercriminals, the travel industry has become a lucrative new target and it’s not hard to see why. Big money, emotional stakes, digital self-service, and a globally distributed ecosystem of users and suppliers make the perfect storm for fraudsters.
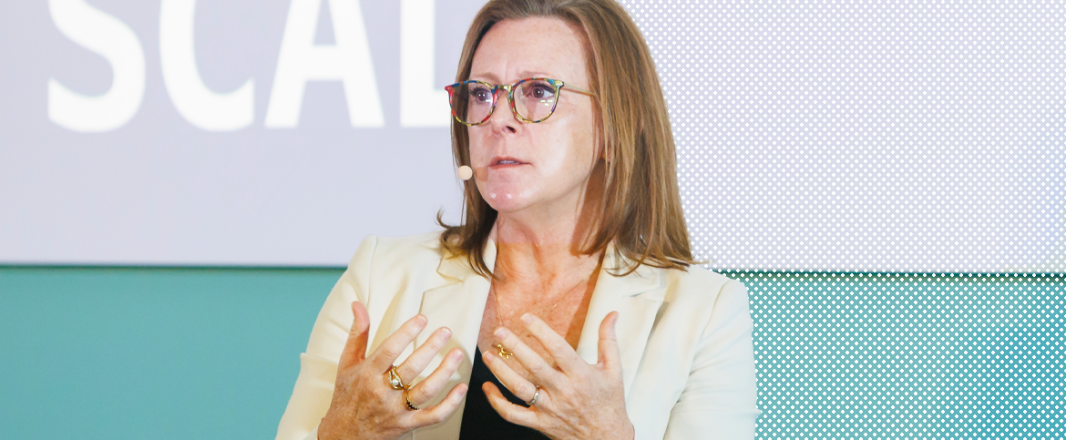
At the centre of the fight is Marnie Wilking, Chief Information Security Officer of Booking.com. With a career that spans cybersecurity roles in finance, healthcare, and e-commerce, Wilking now leads one of the most complex security operations in travel. Her team covers everything from cyber and fraud protection to trust and safety during the guest’s stay and even physical security for employees.
“My job is to create a trustworthy ecosystem with customers and partners and make every experience safe and secure,” she said at Phocuswright Europe in Barcelona in June.
Why travel has become a prime target
While travel isn’t yet the most targeted industry, it’s increasingly under threat. “Historically, cybercriminals have gone after banks, governments, and healthcare,” Wilking noted. “But in recent years, travel has become much more attractive, particularly after COVID and the revenge travel boom.”
What makes travel especially vulnerable?
- High emotion and urgency: Travellers have often invested substantial money and emotional capital into their trips. If a scammer sends a fake cancellation notice, they panic and click.
- Hospitality mindset: Suppliers in the travel space are wired to help. “When a scammer sends a fake email to a hotel pretending to be a customer, saying they’ve attached an encrypted map, the hotel opens it because they want to help,” Wilking explained. That opens the door to malware and account takeovers.
The rise of Generative AI and deep phishing
Depending on what research you look at – some say phishing has decreased by 300%, some say it’s increased by 2,000% – but what’s clear is that since November 2022, coinciding with the launch of ChatGPT, “it’s increased significantly”, said Wilikng.
Attackers now have “the ability to create more real looking phishing emails in multiple languages that are that have better grammar, so they’re a lot harder to spot. So, if you feel like you’re seeing more spam and phishing emails hitting your inbox and not getting cleaned up by your email provider – it’s happening,” she added.
Fake listings and fraudulent hosts
The image-driven nature of travel e-commerce also makes it vulnerable. With generative AI tools, it’s now easier than ever to fabricate enticing property images or listings that look legitimate but don’t exist.
With Booking.com’s push into alternative accommodation, the challenge of verifying new hosts is increased. While the company wants to onboard legitimate property owners quickly, that speed is a double-edged sword.
“There’s a balance – we have seen an increase in fake properties being listed but how much friction do we add to the listing process versus how we make sure that people get online” and have a good, safe experience.
She spoke of a three-prong approach – prevention, detection, education.
“From a prevention standpoint – bad guys are using AI. We’re definitely using AI as well to detect fake workers and fake properties, and over the course of the last couple years, as we have improved our models and leveraged some outside vendors as well, we’ve been able to block about 99% of fake bookings.”
That remaining 1% is still a problem, especially when volumes increase during peak seasons.
The company also uses signals like location mismatches (e.g. a host address in one region but a bank account elsewhere) to detect fraud.
The 50 million message problem
Perhaps the most staggering statistic from Wilking’s session: in just one recent month, Booking.com blocked 50 million phishing attempts via its own internal messaging systems.
These often come from compromised partner accounts, targeting guests with fake links. Booking.com now uses AI to scan messages and block malicious URLs, sometimes redacting the entire link.
But even then, scammers adapt, and users don’t always help.
“We saw one case where a traveller asked the scammer to send the redacted link via WhatsApp,” she said. “That’s how convinced they were that it was a real hotel.”
One-Time passwords and passkeys
In response to credential stuffing – a technique where hackers use stolen email/password combos from breaches to log into multiple sites – Booking.com has rolled out stronger login controls.
“We implemented one-time passwords, which significantly reduce risk unless scammers have access to your email,” said Wilking. The company also recently introduced passkey login support, using the user’s device as a secure authenticator.
She advises all users, both consumers and partners, to enable multi-factor authentication (MFA) wherever it’s offered.
Nation-state actors and the supply chain risk
The threats don’t stop at phishing and fake listings. Wilking revealed that nation-state attacks are growing, particularly those originating from North Korea.
“North Korea has sent workers to apply for and get remote tech jobs,” she said. “The devices are shipped to a laptop farm, and someone else does the job remotely, with the earnings funneled back to the regime. One ring sent an estimated $17 million over several years.”
These attacks often aim to infiltrate the supply chain, using small vendors as entry points to larger organizations.
Educating the ecosystem
Beyond technology, Wilking believes education is a crucial pillar of defense.
Her team pushes regular updates via the Booking.com Partner Hub, adds banners to guest interfaces, and participates in information-sharing groups like the Retail & Hospitality ISAC (Information Sharing and Analysis Center).
“Not all companies have dedicated security teams,” she said. “By sharing intelligence, IP addresses, scam patterns, we can raise the tide for everyone.”
That includes consumers. “We’re very clear that our systems haven’t been breached,” she emphasized, “but attackers are learning to mimic platforms and trick people outside the system. That’s where education plays a huge role.”
Advice for Travellers and Providers
Wilking wrapped with three critical pieces of advice for anyone navigating the digital travel landscape:
- Always use multi-factor authentication.
- Keep apps and software up to date.
- Be suspicious of urgency. If it feels too good to be true or too urgent to ignore, it probably is.
“Scammers are always evolving, but we are too,” she said. “With the right mix of prevention, detection, and education, we can make the digital travel ecosystem safer for everyone.”
Watch full interview here: